Executive Governance
Clear reporting, accountable ownership, risk acceptance, and decisions leadership can defend.
 814North
Fractional CISO leadership for healthcare
814North gives hospitals and healthcare organizations the security leadership to turn cyber risk, HIPAA obligations, vendor exposure, and AI adoption into clear, accountable action.
Where security becomes leadership
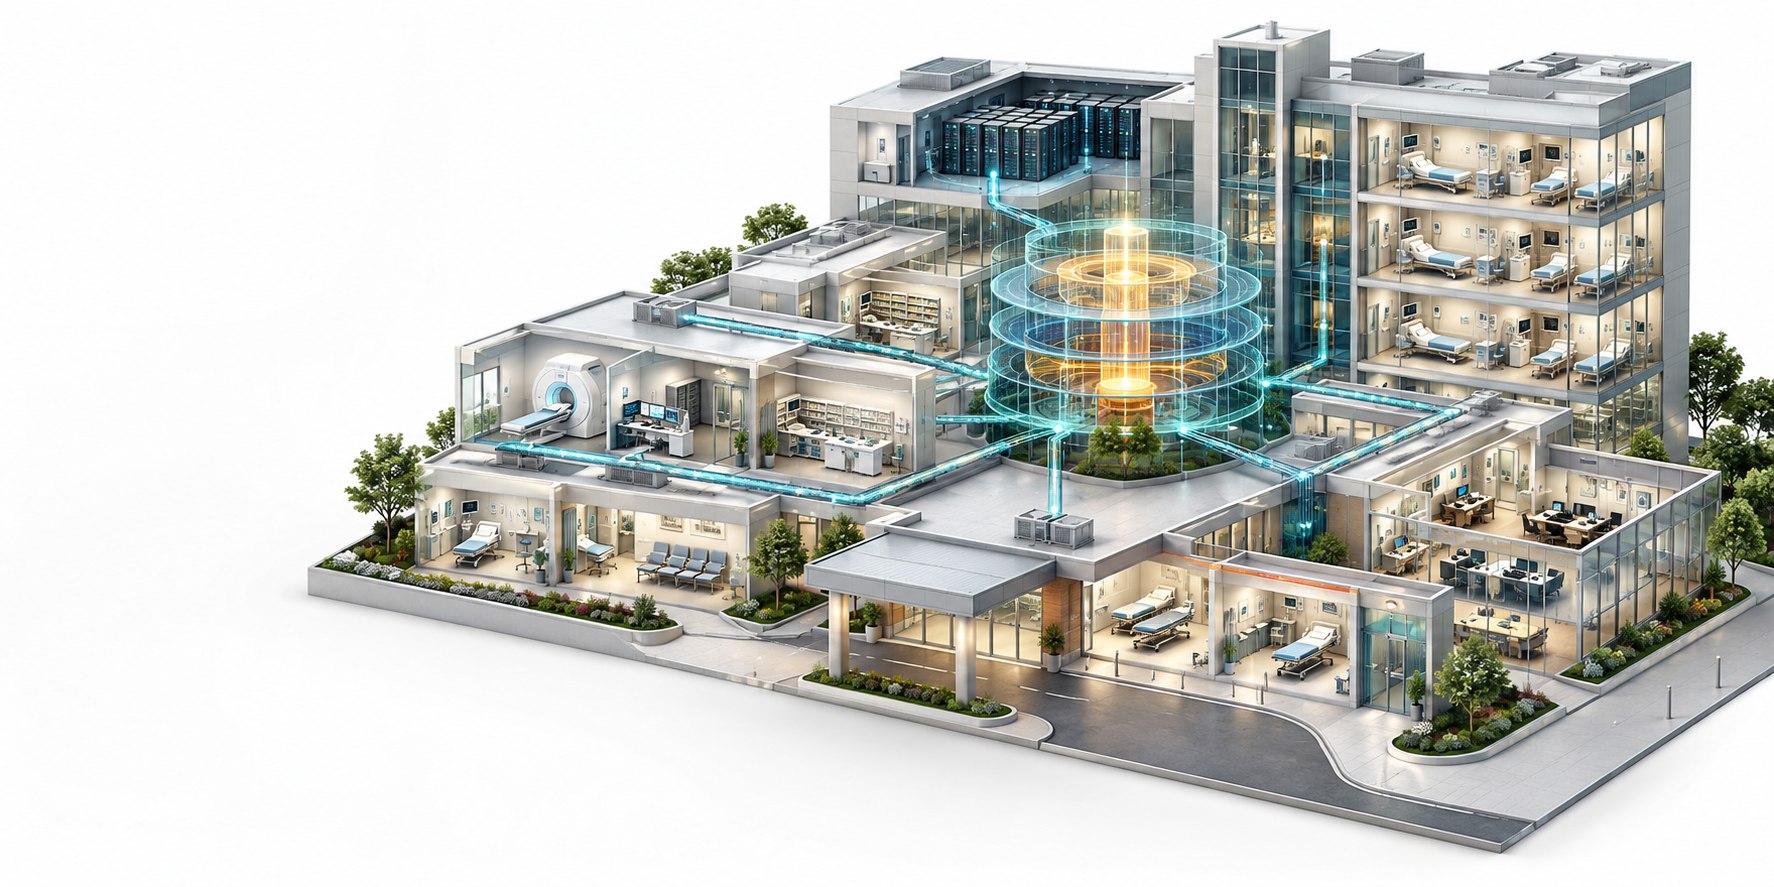
Every risk touches something real: patient care, clinical uptime, privacy, revenue, reputation, or the ability to operate.
814North connects technical reality to executive responsibility so leaders can see the risk, make defensible decisions, and keep the organization moving forward.
One operating model
Policies, controls, evidence, owners, and priorities work together as one security program. Nothing lives in a binder simply to satisfy an audit.
Clear reporting, accountable ownership, risk acceptance, and decisions leadership can defend.
Security Rule alignment, evidence, audit readiness, and policies connected to real operations.
Technical, operational, third-party, and AI risks translated into priorities that can move.
Incident readiness, vulnerability management, architecture, and control maturity kept aligned.
Due diligence, contract expectations, remediation tracking, and evidence for critical partners.
Requirements people can follow, leaders can enforce, and reviewers can understand.
Responsible AI in healthcare
814North helps healthcare organizations understand where AI is already being used, evaluate vendors and data handling, define approved use, protect PHI, require human oversight, and distinguish assistive tools from autonomous action.
What changes
Technical findings become business decisions with context, ownership, and a path forward.
Resources follow clinical impact, regulatory exposure, and operational consequence.
Incident roles, evidence, vendor expectations, and policy are established before pressure arrives.
The program is understandable to executives, workable for technical teams, and defensible under review.
Fractional by design
814North is built for healthcare organizations that need experienced security leadership, but do not need another full-time executive seat. The engagement stays focused on decisions, progress, and measurable program maturity.